Fraud prevention has entered a different phase. It is no longer banks against fraudsters with outdated tools. Both sides are now using AI, and the pace of change on the attack side has pulled ahead in meaningful ways.
According to Mastercard’s payment fraud prevention report, organizations lost an average of $60 million to payment fraud in the past year. In the US alone, fraud losses could hit $40 billion by 2027, driven largely by generative AI, according to Deloitte’s Center for Financial Services.
In response, 91% of US banks currently use AI for fraud detection. The shift isn’t just about scale. It is about what attacks now look like and how fast they evolve. Fraud today adapts in real time and originates from tools specifically built to slip through static defences.
The challenge for banks and financial institutions (BFSI) is building defences that keep up. That starts with understanding the threat landscape, then knowing what tools, models and infrastructure are actually needed to act on it. This blog covers both.
AI-powered fraud detection helps financial institutions improve detection accuracy by continuously analyzing new transaction patterns, behavioral signals and emerging fraud risks.
Part 1: Attack & defence, dual roles of AI in modern financial fraud
How AI Is being used to commit fraud
The nature of financial fraud has shifted. It is not just that attacks are more frequent; it is that they are more convincing, more automated and much harder to catch using traditional methods.
Tools like FraudGPT and WormGPT are purpose-built for financial crime. They generate phishing emails, fake invoices and scam scripts quickly, without requiring any technical background. AI image models take this further, producing bank statements, pay stubs and utility bills that are pixel-generated from scratch, not edited from real files. Visual review alone cannot catch these.
These are not niche threats. Attack kits are sold as subscriptions on underground forums, which means large-scale, coordinated fraud campaigns are now within reach of almost anyone. Banks are dealing with higher volumes of fraud attempts arriving in forms that require verification upfront, not just detection after the fact.
The specific attack surfaces that have opened up as a result:
- AI-generated documents: Fake financial documents produced by AI models are increasingly indistinguishable from genuine ones, making traditional verification methods unreliable.
- Deepfake identity fraud: Voice and video generation tools are now widely accessible, enabling identity impersonation at onboarding and authentication stages.
- Fraud-as-a-service: Subscription-based attack tools lower the barrier to entry, enabling coordinated campaigns at a scale that was previously difficult without deep technical expertise.
- Adaptive attacks: Unlike older fraud patterns that stayed fixed, AI-driven attacks can adjust in real time in response to detection signals, making them harder for static systems to catch.
Where rule-based systems fall short
Rule-based systems work on fixed conditions: a transfer above a certain amount, a login from an unusual location. For well-documented fraud patterns, they remain useful. The problem is everything outside those predefined conditions.
When fraud does not match an existing rule, it passes through undetected. When a legitimate transaction happens to match a rule, it gets flagged, adding to manual review queues and causing friction for genuine customers. And every new fraud pattern requires a new rule to be written, tested and deployed, a process that consistently falls behind how quickly attack methods change.
AI does not replace rule-based systems. It fills the gaps they leave. Rather than checking a transaction against a fixed condition, AI evaluates the full context: behavioural history, transaction timing, peer-group norms, device data. Fraud signals that have no rule attached to them get surfaced. Detection shifts from reactive to adaptive, and the system improves over time without needing to be manually updated every time a new fraud type emerges.
Where AI is making a difference: use cases for BFSI
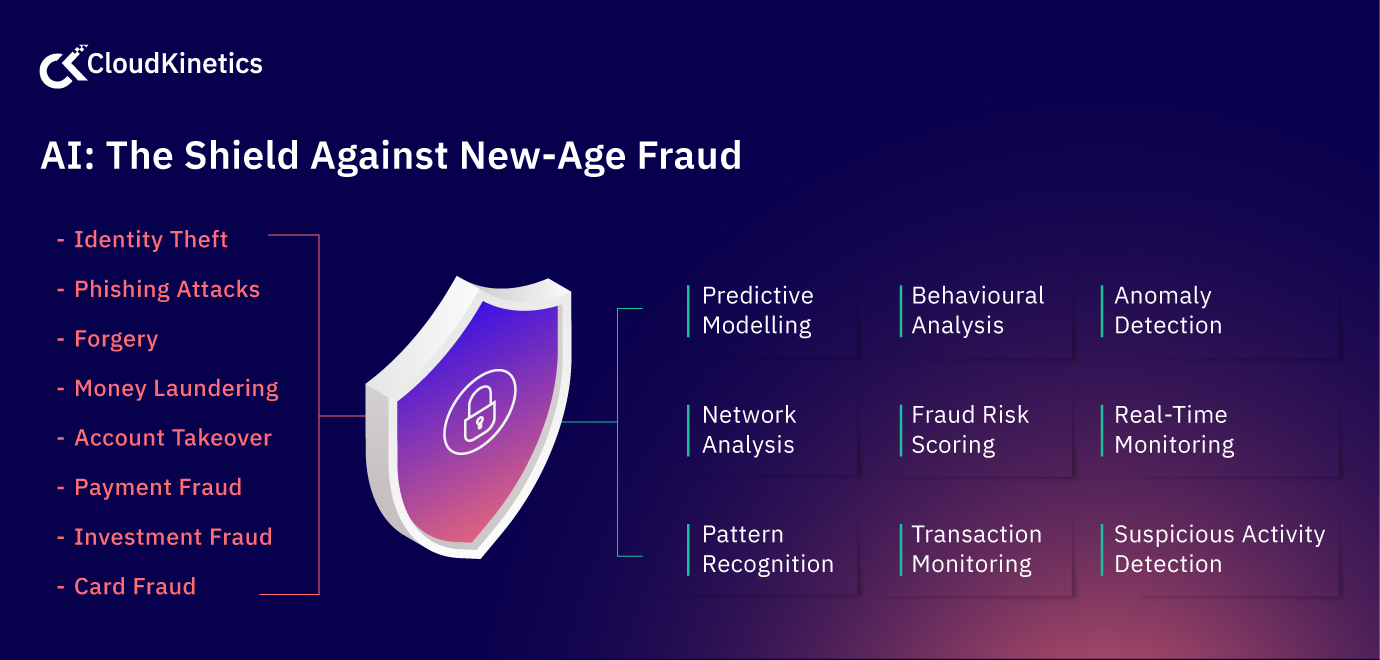
The same capabilities that make AI effective for fraud are what make it effective against fraud. Financial institutions are deploying AI across the full transaction lifecycle, from real-time detection at the point of a transaction to investigation and reporting after a case is flagged.
Real-time anomaly detection
AI learns what normal behaviour looks like for each customer: their typical spending range, login times, transaction geographies. When something falls outside that pattern, it gets flagged immediately. An account takeover attempt might use valid credentials but initiate a transaction type the customer has never made. That discrepancy, invisible to a rule-based system, gets caught in real time.
Automated fraud reporting
AI and ML reduce the time fraud teams spend on routine review. Suspicious activity reports (SARs) can be generated automatically, incorporating large volumes of data that would take analysts hours to process manually. With lower-risk alerts filtered out, teams can focus on cases that genuinely need human judgment.
Enhanced authentication
AI refines biometric verification, from facial recognition to voice ID, and helps identify anomalies even when valid credentials are used. This is particularly relevant for account takeover fraud, where stolen credentials are the entry point. An AI system can detect that the person using those credentials does not behave the way the account owner normally does.
Behavioural pattern detection
AI picks up on signals that manual review misses entirely: device fingerprint, screen resolution, language settings, transaction timing. In cases where a customer’s banking details are compromised outside the bank’s own systems, AI-based monitoring can still flag unusual patterns and trigger verification. Traditional systems, checking only for predefined conditions, would not catch this.
Offline fraud detection
AI extends into physical channels through video analytics. Suspicious behaviour at ATMs and branches, skimming activity, stolen card usage and cheque forgery can be flagged before damage is done, not after.
Part 2: Building the defence for BFSI: Models, infrastructure & a practical roadmap
The AI models available for fraud detection
No single model covers every fraud type. Banks that have moved beyond pilots are typically running a layered architecture, where different models handle different detection tasks. Here is what that stack looks like and where each model type is most effective.
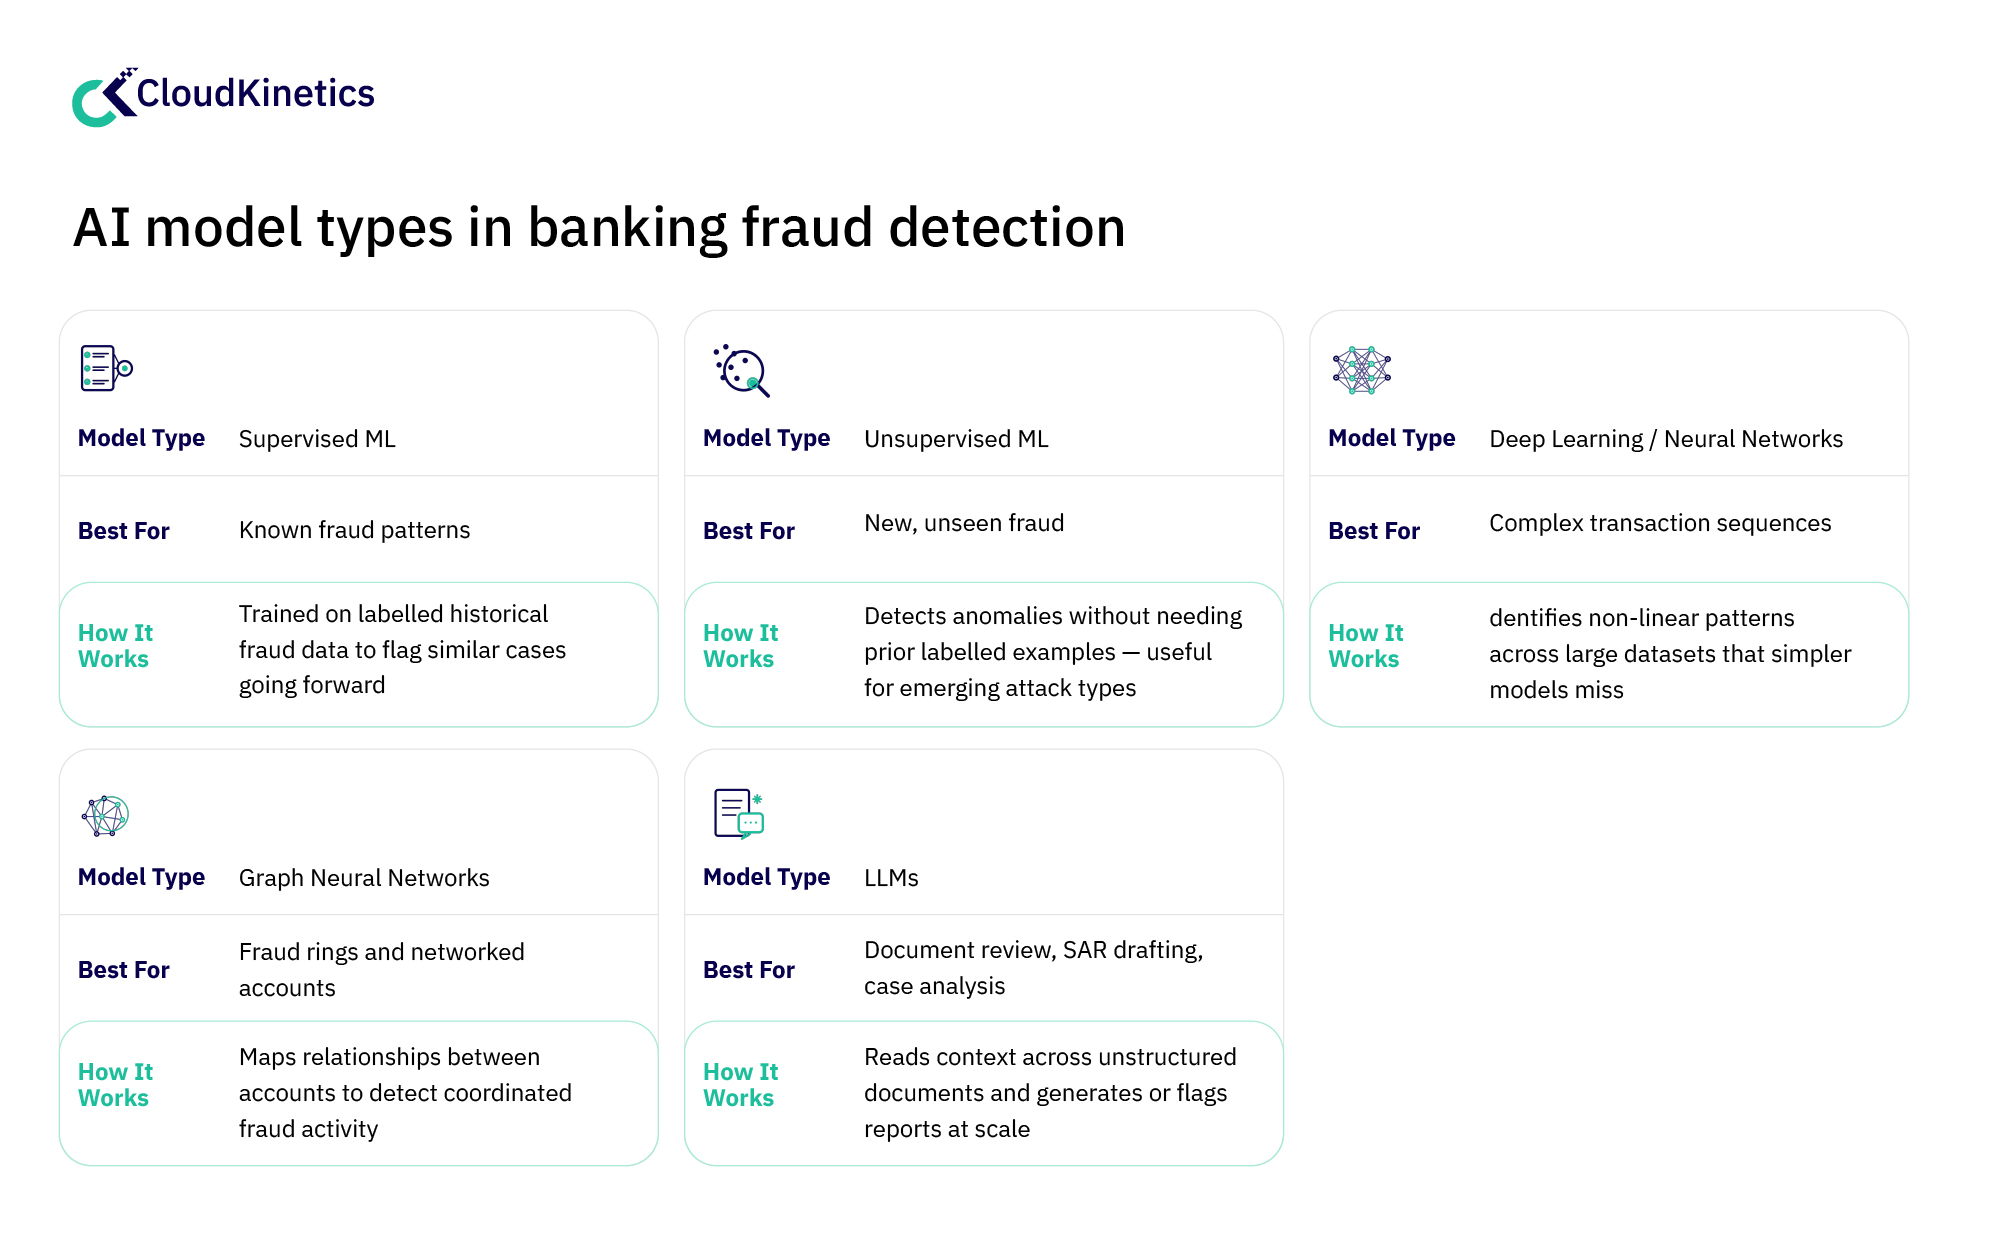
Each model addresses a gap the others leave. Supervised models are strong against known repeat fraud patterns. Unsupervised models catch first-time fraud with no prior example to match against. Graph neural networks are built for fraud rings, situations where multiple accounts are linked through shared devices, IP addresses, or documents, but each individual account looks clean on its own. LLMs bring a different kind of value: reading unstructured case history, cross-referencing documents and producing draft SARs far faster than manual review allows.
Layered together, these models shift fraud detection from isolated transaction checks to a connected view of risk across accounts, documents and networks.
Reducing false positives
A false positive is more than a technical error. When a legitimate transaction is blocked, a customer is frustrated, an analyst’s time is consumed, and a review is opened that should never have existed. Multiply that across transaction volume and the operational cost adds up quickly.
The deeper issue with static rule-based systems is that they apply the same condition to every transaction regardless of context. A transaction that hits a threshold triggers an alert whether or not anything else about it looks suspicious. AI changes this by evaluating the full picture before deciding whether to intervene. Spending history, device fingerprint, geographic context, transaction timing, these signals, taken together, allow the model to distinguish a genuinely unusual transaction from one that simply looks unusual in isolation.
The results are measurable. According to Feedzai’s AI Fraud Trends report, 90% of financial institutions are now using AI to expedite fraud investigations and detect new tactics in real time, with adoption running at 50% for scam detection, 39% for transaction fraud and 30% for anti-money laundering.
For fraud teams, fewer false positives mean fewer cases in the queue and faster resolution on the ones that genuinely warrant attention. For customers, it means fewer legitimate transactions wrongly declined, a direct connection between fraud accuracy and customer experience.
What fraud detection looks like when it is actually in production
Pilot programs tell you whether an approach is promising. Production deployments tell you whether it works at scale. A few institutions have crossed that line, and the results are worth looking at.
Mastercard uses AWS AI and ML services to power fraud detection across its global network. The outcome: three times more fraudulent transactions detected and a tenfold reduction in false positives. That translates into billions of dollars in merchant savings and significantly fewer legitimate transactions wrongly declined.
NatWest Group has deployed close to 100 ML models on Amazon SageMaker, with plans to scale to thousands over the next two years. The models run across its 20-million-customer base, supporting more personalized communication alongside fraud reduction. One measurable side effect: customers in lower-income neighbourhoods saved close to half a million pounds in ATM fees within six months.
What both cases have in common is where fraud detection sits in the stack. It is built into the cloud infrastructure, not added onto legacy systems afterwards. That distinction matters more than it might appear.
The infrastructure that makes real-time detection possible
AI fraud detection depends on three infrastructure layers working together. If any one of them is weak, the model performance suffers regardless of how well the model itself is built.
The first is a unified data platform, typically hybrid or multi-cloud, that gives models a real-time, consistent view of transaction data across all systems. Without this, models are working with fragmented or delayed data, which undermines their ability to detect anything in the moment it is happening.
The second is scalable compute. Inference needs to happen at the moment a transaction occurs, not in batch cycles hours later. The infrastructure needs to handle peak transaction volumes without lag.
The third is governance. For regulated financial institutions, data lineage, access controls, and audit trails are not optional additions. They need to be part of the infrastructure design from the start. Institutions that treat governance as an afterthought often find it becomes the bottleneck that prevents the whole system from performing as expected in production.
The way these three layers connect, how the data platform feeds the model and how audit controls sit across both, is ultimately what determines whether a fraud detection program delivers in a real environment.
A practical roadmap for building AI fraud defence
AI fraud detection is not a single deployment. It requires coordinated decisions across teams, data infrastructure and processes. The institutions that get this right treat it as a program, not a project.
| Step | What It Involves |
| Cross-functional team | Bring together IT, compliance, legal, operations and data science. Fraud strategy that sits in one function tends to miss the context that other functions hold. |
| Multi-layered detection | Combine AI models with encryption, multi-factor authentication and existing anomaly detection. No single layer catches everything. |
| Right infrastructure | Choose tools that work with existing systems and can scale as transaction volume grows. Real-time inference requires infrastructure designed for it from the ground up. |
| Ethical data use | Follow customer privacy norms, maintain transparent data usage practices and stay current with regional data regulations. |
| Continuous monitoring | Retrain models regularly against new fraud patterns. AI systems that are not updated become as rigid and exploitable as the rule-based systems they were meant to replace. |
| Simulations | Run controlled fraud attack tests periodically. Knowing where gaps exist before attackers find them is far less costly than discovering it the other way. |
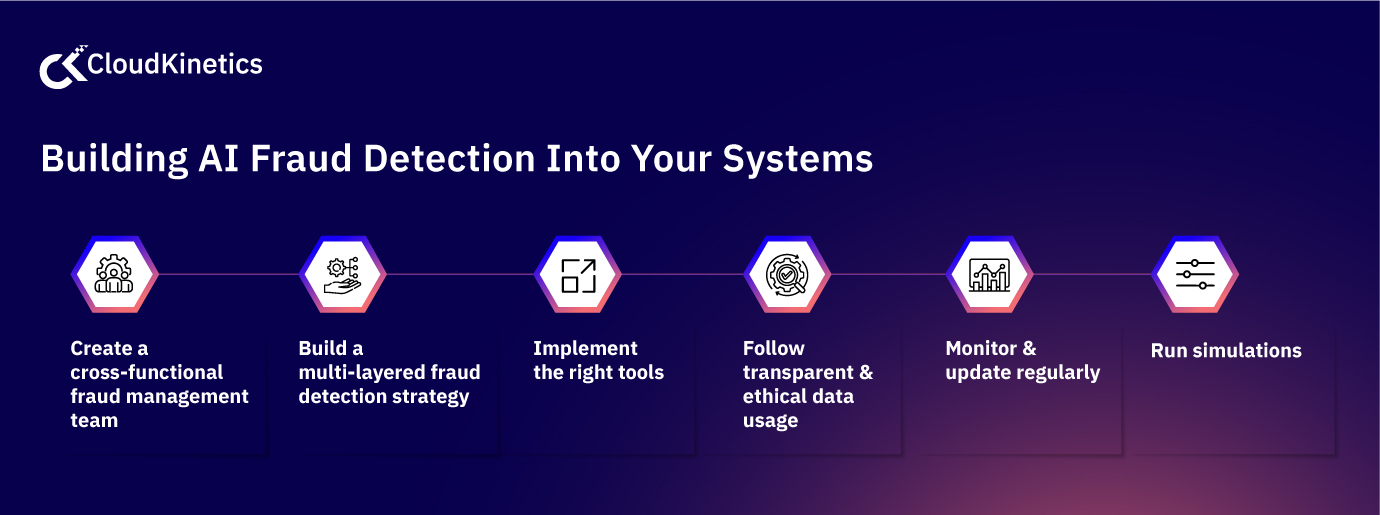
Beyond the technical framework, the human layer matters too. AI handles pattern recognition at scale. It does not replace the judgment calls, the cross-team communication, or the security culture that determines how well a team actually responds when something gets through. Regular training and a shared sense of responsibility across the organization are what close the gap that no model can.
Conclusion
Fraud has always been an arms race. What has changed is the pace. AI has given attackers tools that scale, adapt and arrive in high volume. Banks and financial institutions that are winning are the ones that have stopped thinking about fraud detection as a single system and started treating it as a connected program: threat awareness, the right model architecture, the right infrastructure and a team that can keep all of it current.
The good news is that the same AI capabilities being used to commit fraud are available to defend against it. The difference between institutions that are ahead of this and those that are not often comes down to where they started: with the data infrastructure and governance layer in place, or trying to retrofit it later. For financial institutions looking to move from reactive to adaptive fraud defence, the path starts with getting the foundation right.
If you work in BFSI and are thinking through how to make this work for your organization, Cloud Kinetics’ financial services practice focuses specifically on building the cloud infrastructure, data pipelines and governance layer that AI-driven fraud detection depends on. Explore how we work with financial services: Cloud Kinetics for Financial Services.